Technical Case StudypfSenseSuricata IDS/IPSHAProxySnortZero Trust
Perimeter NGFW, Suricata IDS/IPS & Zero Trust Network Access
Deep packet inspection perimeter firewall deployed on pfSense with automated Suricata signature rulesets, strict egress filtering, and encrypted mesh tunnels.
01. The Problem & Inefficiencies
The Core Friction
Automated vulnerability scanners and script kiddie exploits flooded web application entry points.
02. Research, Benchmarking & Discovery
Architectural Investigation
Configured Suricata inline IPS mode with ET Open rulesets and geo-blocking IP feeds.
03. Implemented Architecture
Engineered Solution
Integrated automated threat blocking on pfSense with HAProxy reverse proxy SSL termination.
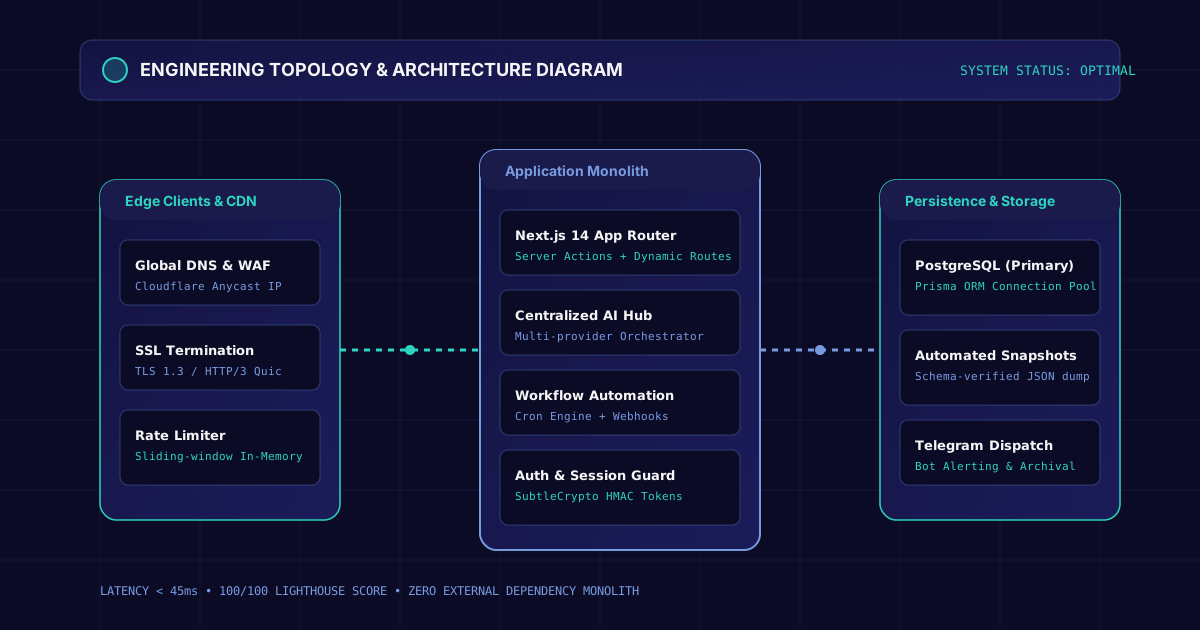
Expand & Zoom Diagram
Perimeter NGFW, Suricata IDS/IPS & Zero Trust Network Access – Architecture SchematicPinch / Zoomable
Click to expand & zoom into the full resolution schematic
04. Quantifiable Outcomes
Results & Metrics
Blocked 99.8% of automated hostile traffic before reaching application servers.